Credential hygiene in 2026 refers to the proactive management of user identities to prevent account takeovers and reduce administrative overhead. For UK organisations, the most effective strategy involves combining Single Sign-On (SSO) with Self-Service Password Reset (SSPR). SSO improves security by reducing the "password surface area"—the number of unique credentials a user must remember—while SSPR empowers users to resolve lockouts independently. When aligned with Cyber Essentials v3.3 standards, these tools eliminate weak password reuse and significantly reduce helpdesk tickets, ensuring that security protocols do not hinder institutional productivity.
The Hidden Cost of "Dirty" Credentials
In the modern UK educational and public sector landscape, "dirty" credentials—passwords that are weak, reused, or poorly managed—represent the single greatest vulnerability to network integrity. However, the cost of poor credential hygiene is not only measured in security breaches; it is measured in the erosion of institutional resources.
The Helpdesk Drain
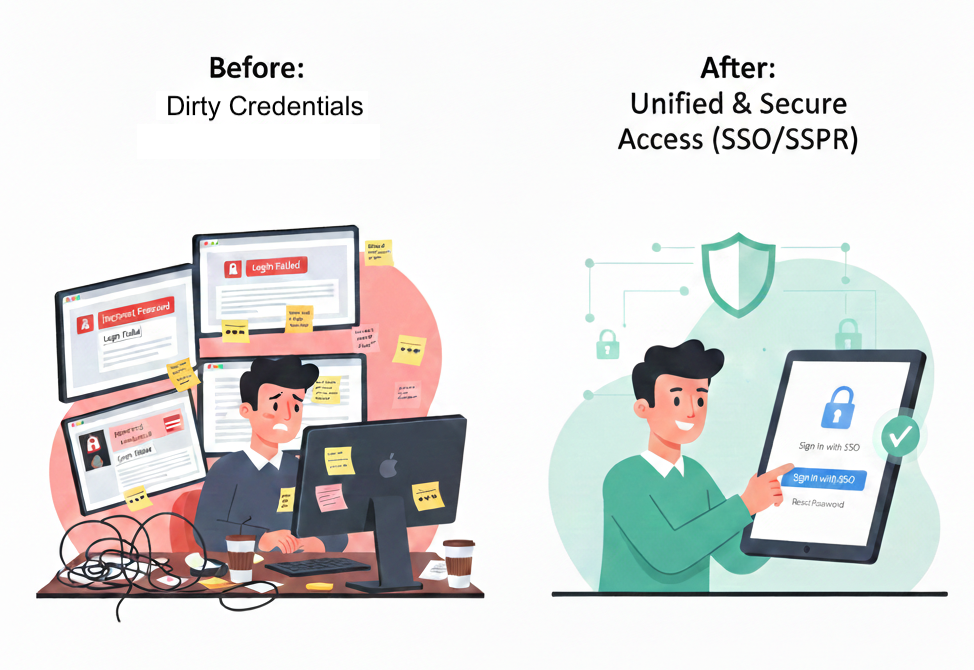
Industry data leading into 2026 suggests that a single password reset can cost an organisation up to £50 when accounting for the lost productivity of the user and the time allocated by the IT support professional. For a large university or a local council with thousands of users, a single "back-to-term" week can result in hundreds of these requests. This is a significant drain on budgets that could otherwise be allocated to digital transformation or infrastructure improvements.
The Vulnerability of Reuse
Credential stuffing remains a primary threat vector. If a member of staff uses the same password for a personal shopping account as they do for their institutional access, a breach at a third-party retailer becomes a direct threat to your internal systems. Single Sign-On (SSO) addresses this by ensuring that the user only has one "Master" credential to protect, which can then be fortified with robust Multi-Factor Authentication (MFA).
The "Shadow IT" and Physical Risk
When IT departments enforce complex password rotation policies without providing a tool like SSPR, users inevitably create their own "solutions." These often manifest as "Shadow IT"—using unapproved password managers—or, more commonly, physical security risks such as passwords written on notes kept under keyboards. This behaviour is a natural response to "security friction." If a system is too difficult to navigate, users will find a way to bypass the intended security controls.
Taming the Chaos: The Role of SSO (Single Sign-On)
Single Sign-On is no longer merely a convenience for the end-user; it is the cornerstone of a secure 2026 identity strategy. By consolidating multiple entry points into a single, highly protected gateway, UK organisations can enforce rigorous security standards without overwhelming their staff.
Reducing the Attack Surface
The primary benefit of SSO is the drastic reduction of the "attack surface." Instead of managing and securing fifty different login portals for various educational resources or public services, IT teams focus their defensive efforts on one primary identity provider (IdP). This allow for the implementation of phishing-resistant Multi-Factor Authentication (MFA)—now a mandatory requirement for Cyber Essentials v3.3 certification—at the most critical juncture.
Conditional Access in 2026
Modern SSO solutions, such as those provided by Overt Software, go beyond simple username and password checks. We utilise Conditional Access policies that evaluate the context of every login attempt. For example, if a user attempts to log in from an unrecognised IP address outside of the UK, or from a device that does not meet the institution's health standards, the SSO system can automatically deny access or trigger an additional security challenge.
Seamless Federation with the Overt SAAM Bridge
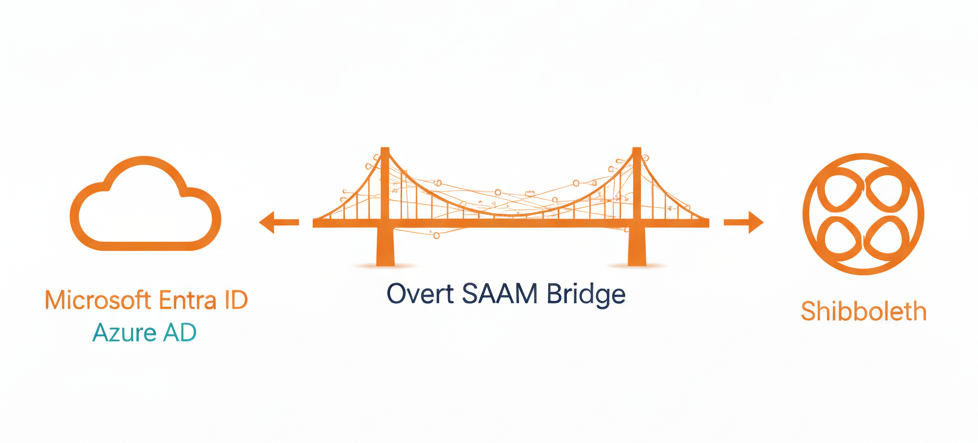
A common challenge for UK Higher Education and Public Sector bodies is the "identity gap" between Microsoft ecosystems (Azure/Entra ID) and research-focused federations like Shibboleth. Our Overt SAAM Bridge acts as a secure translator between these environments. It allows your users to use their familiar Microsoft credentials to access Shibboleth-protected resources seamlessly. This "single set of keys" approach ensures that credential hygiene is maintained across the entire digital estate, not just within a single silo.
Empowering the User: The Logic of SSPR (Self-Service Password Reset)
While SSO secures the entrance, Self-Service Password Reset (SSPR) provides the safety valve. In the 2026 UK landscape, IT departments must transition from being "gatekeepers" to "enablers." Providing a secure, automated way for users to regain access to their accounts is a vital component of this transition.
24/7 Autonomy for a Hybrid Workforce
The traditional "nine-to-five" UK office hour model is increasingly obsolete within the education and public sectors. Staff often prepare lectures in the evening, and students frequently access library resources during weekends. If a user is locked out on a Friday evening and must wait until Monday morning for a helpdesk manual reset, the loss of productivity is substantial. SSPR provides 24/7 autonomy, allowing users to resolve issues in real-time, regardless of when they choose to work.
Identity Verification Protocols
A common misconception is that SSPR weakens security. In reality, a well-configured SSPR system is far more secure than a manual helpdesk reset, which can be vulnerable to social engineering. By using MFA-backed verification, SSPR ensures that the person requesting the reset is indeed the account owner. Users can be required to provide multiple forms of identification—such as an authenticator app code, a biometric scan, or a verified secondary email—before a reset is permitted.
Compliance Alignment with Cyber Essentials v3.3
The Cyber Essentials v3.3 standard (the "Danzell" standard) places significant emphasis on User Access Control. It requires that password recovery methods are as robust as the primary authentication method. SSPR fulfills this requirement by creating an audited, secure workflow for credential recovery. This ensures that your institution does not fail a compliance audit due to "weak links" in the password recovery process.
Information Gain: Unique Insights for 2026
The "Passwordless" Transition
As we move through 2026, the industry is shifting toward Passkeys (FIDO2). SSO acts as the essential bridge for this transition. By implementing an SSO gateway now, your organisation can begin to introduce passwordless logins for specific departments without needing to overhaul every legacy application. This phased approach reduces user shock while drastically improving credential hygiene.
Psychological Security and Friction
There is a documented phenomenon known as "Security Fatigue." When users are forced to interact with clunky, difficult security systems, they become less vigilant. By making the login process "frictionless" through SSO and SSPR, you actually increase the psychological buy-in from your users. When security is easy, users are more likely to follow protocols rather than look for workarounds.
The Audit Advantage of Automation
Manual password resets often leave poor paper trails. In contrast, automated SSPR and SSO activity generate rich, immutable logs. For a 2026 UK auditor, seeing a clear history of how credentials were reset and verified provides instant evidence of "Identity Lifecycle Management." This level of transparency is difficult to achieve without a dedicated automated solution.
Why Overt Software is the UK’s Choice for Identity Management
As we have explored, the transition to superior credential hygiene requires more than just software; it requires a partner who understands the unique architectural needs of the UK public and education sectors. Overt Software Solutions provides the expertise and the specialised tools to make this transition seamless.
The Overt SAAM Bridge: Unifying Your Ecosystem
Many UK institutions find themselves caught between two worlds: the Microsoft-centric administrative environment and the research-focused Shibboleth federation. Our SAAM (Shibboleth Azure AD/ADFS Authentication Module) Bridge is a unique solution designed to eliminate the "double login." It allows your users to authenticate once via Azure AD (Entra ID) and move fluidly into Shibboleth-protected resources like library databases or the VLE.
User-Centric SSPR with Localised Trust
Trust is the foundation of identity management. Overt’s SSPR interfaces are not "off-the-shelf" portals; they are fully customisable and branded to match your institution’s visual identity. This reduces user hesitation during the password reset process, as they can clearly see they are within a secure, official environment managed by their own IT department.
Reliability and Premium Support
When you centralise your credentials through SSO, that system becomes the "keys to the kingdom." If it fails, your institution stops. We provide Premium Hosted Backups and Load Balanced Hosting within state-of-the-art Tier 3/4 Data Centres to ensure 24/7 availability. Furthermore, our Worcester-based team provides unlimited support, ensuring that you always have access to a human expert who understands your specific setup.
Key Takeaways: A Strategy for Stability and Security
Credential hygiene in 2026 is no longer about forcing users to remember thirty-character passwords with symbols and numbers. It is about a strategic shift toward Single Sign-On (SSO) to reduce the attack surface and Self-Service Password Reset (SSPR) to empower your workforce.
By implementing these tools, your organisation does more than just tick a box for Cyber Essentials v3.3; you build a resilient, efficient, and user-friendly digital environment. You save your helpdesk from the "reset loop" and protect your users from the dangers of credential reuse.
Secure Your Organisation's Future with Overt
Is your helpdesk still bogged down by password reset tickets? Are your users frustrated by multiple login prompts? It is time to modernise your identity infrastructure.
- Experience a True Single Sign-On Environment: Contact us to discuss how the SAAM Bridge can unify your Microsoft and Shibboleth resources.
- Request a Custom SSPR Demo: See how our branded, MFA-backed reset portals can give your users 24/7 autonomy.
- Consult with a Specialist: Speak to our UK-based team today to align your identity strategy with the 2026 compliance landscape.
Take the Next Step
Do not leave your sensitive applications vulnerable to AI-driven threats. Contact Overt Software Solutions today for a Strategic Access Review. Our expert engineers will evaluate your current authentication flows and help you implement a risk-based strategy that protects your "Keys to the Kingdom."